
A WordPress hacked redirect sends visitors from your site to a different domain, page, advertisement, or search result. It may affect everyone, only mobile visitors, logged-out users, or traffic arriving from search engines. That variation is intentional in many compromises, which is why the site can look normal when you are logged in.
In this guide
Do not begin by repeatedly deleting suspicious files or reinstalling WordPress. First preserve a backup, identify whether the redirect is happening at the browser, server, or WordPress level, and then clean the complete infection. The steps below focus specifically on redirect malware rather than general site troubleshooting.
1. Confirm that the redirect is really on your site
Test the site from a private browser window and from a second network, such as a phone connection. Check the homepage, a normal post, an image URL, and a page that does not use the same template. Also test while logged out. Avoid clicking the destination if it looks suspicious.
- Record the original URL and the destination URL.
- Note whether the redirect affects desktop, mobile, or both.
- Check whether it occurs only on the first visit or after a delay.
- Test with and without common referral sources, such as a search result or social link.
A redirect that happens only in one browser may be caused by a browser extension, cached script, or local DNS issue. If multiple devices and networks show the same behavior, treat the site as potentially compromised.
2. Put the site into a controlled state
Make a complete backup of the files and database before changing anything. Keep one untouched copy for investigation and create a separate working copy for cleanup. A backup made after infected files have been overwritten is much less useful.
If visitors are being sent to phishing pages or malware, temporarily restrict access with your host, a maintenance rule, or a security control. Do not rely on a WordPress maintenance plugin if WordPress itself may be compromised. Ask your host whether they can provide a server-level temporary block or a clean restore point.
Change passwords from a trusted device for hosting, SFTP or FTP, the database, WordPress administrator accounts, and any security or CDN service. Use unique passwords and remove unknown administrator accounts, but preserve evidence before deleting users where possible.
3. Find where the redirect is being injected
A redirect can be created in several layers. Check each layer instead of assuming the problem is a single plugin.
Browser and cache layer
Clear the browser cache, test privately, and purge page-cache, server-cache, and CDN-cache layers. A cached malicious response can make a fixed site appear infected. However, cache purging alone does not clean the underlying site.
Server configuration layer
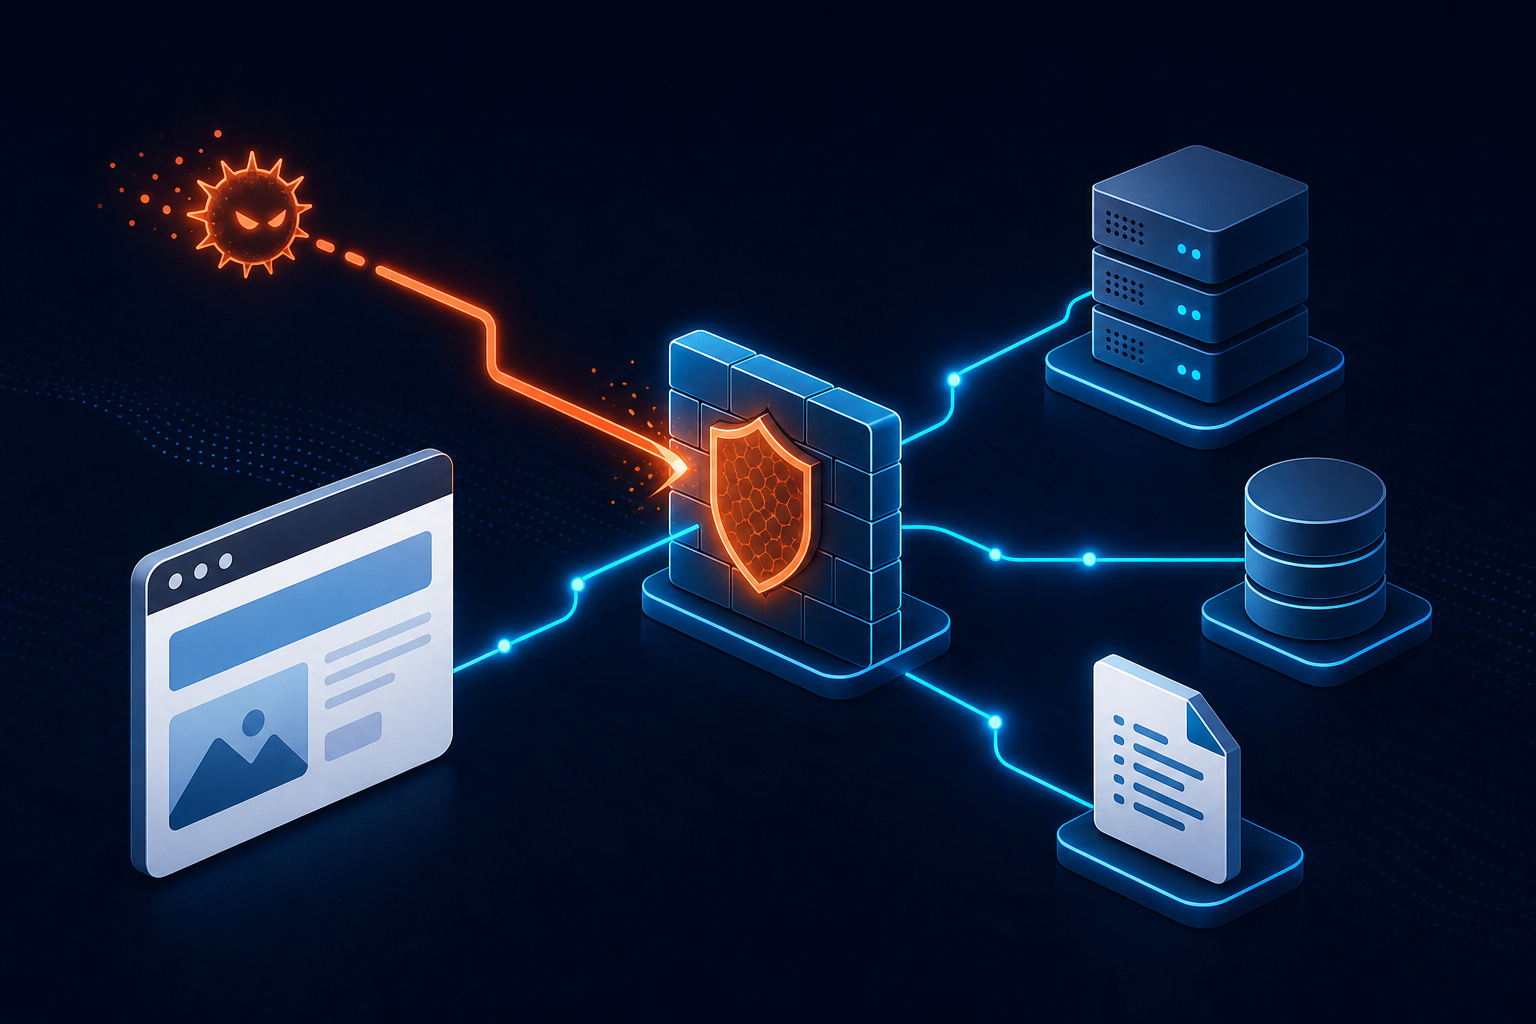
Inspect the document root’s .htaccess file and any server configuration managed by your host. Look for unfamiliar rewrite rules, encoded text, conditions based on user agents or referrers, and redirects to domains you do not recognize. Compare the file with a known-good WordPress configuration, but do not overwrite custom rules blindly.
Also check for additional .htaccess files in wp-content, wp-includes, upload directories, and other directories where they do not belong. An attacker may use a nested rule to redirect only specific URLs.
WordPress database layer
Inspect the site URL settings, active plugins, widget content, menus, theme options, and posts for unexpected scripts or links. Pay special attention to options containing long encoded strings, unfamiliar JavaScript, or domains unrelated to the site.
PHP and JavaScript file layer
Compare WordPress core, plugin, and theme files with clean copies of the same versions. Suspicious indicators include recently modified files, PHP files in upload directories, new files with random names, and code using functions such as eval(), base64_decode(), or gzinflate(). These functions are not automatically malicious, so investigate their context rather than deleting every match.
4. Check the most common redirect locations
Start with files that execute on nearly every request:
wp-config.php, especially code added before the opening PHP tag or after the normal configuration.- The active theme’s
functions.phpand included PHP files. wp-content/mu-plugins, because must-use plugins can run without appearing in the regular Plugins screen.- Regular plugins, especially those installed or modified shortly before the redirect began.
wp-content/uploadsand other writable directories containing unexpected PHP files..htaccessfiles in the web root and nested directories.- Database options and content containing the redirect domain or injected script.
File timestamps can help establish a timeline, but they are not proof: an attacker can alter timestamps, and a legitimate update can modify many files. Use timestamps together with file comparison, access logs, and known-good backups.
5. Remove the infection safely
The safest cleanup is usually to replace compromised WordPress core files with clean copies, reinstall trustworthy plugins and themes, and manually review custom code. Do not replace wp-content/uploads wholesale if it contains important media; inspect it for executable files instead.
Disable suspicious plugins before deleting them. If you cannot access the dashboard, rename a plugin directory through SFTP or your hosting file manager to disable it temporarily. This is a diagnostic step, not proof that the plugin caused the compromise.
Restore a clean .htaccess only after saving the infected copy for reference. Then go to Settings → Permalinks and save the settings once to allow WordPress to regenerate its normal rewrite rules. Exact menu labels can vary by WordPress version and hosting setup.
Remove unknown administrator accounts, unauthorized scheduled tasks, rogue cron entries, and unfamiliar server-level users. Review hosting cron jobs as well as WordPress cron events; a reinfection mechanism can recreate the redirect after the visible code is removed.
For a serious compromise, use a professional WordPress malware removal service rather than deleting files one at a time. Redirect malware often includes more than one persistence method, and incomplete cleanup can leave visitors exposed.
6. Verify the redirect is gone
After cleanup, verify from several independent perspectives:
- Open the homepage and multiple inner pages while logged out.
- Test private browsing on more than one browser and device.
- Check mobile and desktop traffic separately.
- Use a plain HTTP request tool or browser developer tools to inspect the redirect chain and status codes.
- Purge every relevant cache, including CDN and host caches.
- Review server access logs for requests to the malicious destination or repeated suspicious files.
- Confirm that your homepage, site URL, canonical URLs, and redirects point to your own domain.
If the redirect returns after a clean restore, do not keep restoring the same backup. Look for a stolen hosting credential, vulnerable plugin, unknown administrator, cron job, compromised computer, or another site in the same hosting account.
7. Prevent another hacked redirect
Update WordPress, plugins, themes, and the server’s supported PHP version after confirming compatibility. Remove software that is abandoned, nulled, or no longer needed. Limit administrator accounts and enable two-factor authentication where available.
Use separate credentials for hosting, SFTP, databases, and WordPress. Restrict file editing from the dashboard when appropriate, use least-privilege file permissions, and keep tested off-site backups. Monitoring should check both page content and redirect behavior, including logged-out and mobile requests.
For a broader recovery process, see How to Safeguard and Fix Your Hacked WordPress Site. If your site is maintained for clients or you manage several installations, a WordPress care and Site Manager plan can provide ongoing updates, monitoring, and support after cleanup.
When a redirect is not caused by WordPress malware
Not every redirect indicates a hack. A legitimate redirect may come from a changed domain, an intentional URL migration, a host rule, a CDN setting, or a browser extension. Compare the response headers and redirect chain, inspect your domain and DNS settings, and ask your host whether a server-level rule is active.
If the site also shows an HTTPS loop, investigate that separately using the WordPress redirect-loop troubleshooting guide. If URLs resolve to duplicate versions rather than an unrelated malicious domain, review broken canonical tags and duplicate URL issues. For WordPress-specific background and recovery references, consult the official WordPress Documentation.
Quick recovery checklist
- Confirm the redirect on multiple devices and networks.
- Save clean and infected backups before editing.
- Change hosting, SFTP, database, and WordPress credentials.
- Inspect
.htaccess, core files, plugins, themes, uploads, and database content. - Replace compromised software with known-good copies.
- Remove unauthorized users, cron jobs, and persistence mechanisms.
- Purge caches and test logged-out mobile and desktop requests.
- Update software and continue monitoring for reinfection.